What a Kid’s Toy Just Taught Me About Enterprise AI Security
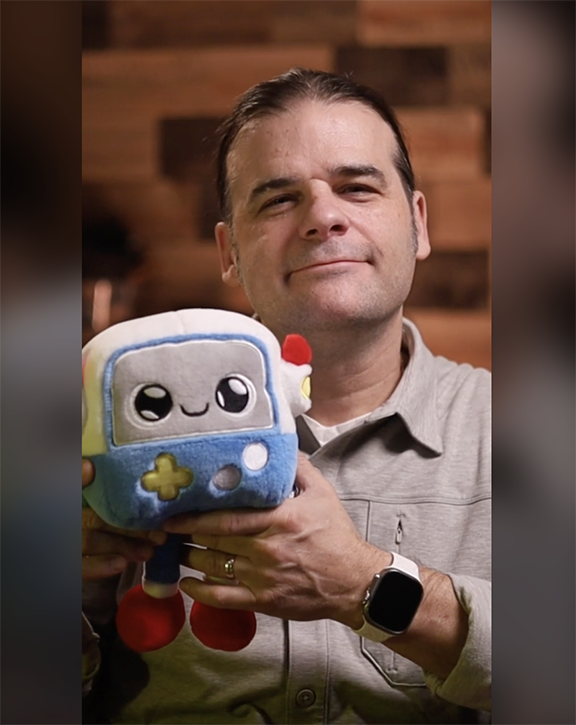
Not long ago, I shared a video of Gabo, a stuffed toy robot made by Kurio. Gabo isn’t your typical kids’ toy. There are no prerecorded phrases, no buttons, no scripted responses. Gabo engages in real, back-and-forth conversations powered by an AI language model built directly into the toy. The same technology behind enterprise customer support tools and business automation, running in a huggable robot sitting on your couch.
 That first video sparked a lot of conversation, and for good reason. For most people, AI still feels abstract, something happening in data centers, boardrooms, and research labs. Gabo makes it tangible. It is something you can hold, talk to, and watch your kids interact with. And that concreteness has a way of sharpening the questions we should all be asking about where this technology is headed.
The question I ended that first video with was a straightforward one for parents: would you allow your child to play with an AI toy like this without supervision? It’s a question worth pondering because the answer likely hinges on how much you trust the safety features built into it.
The future shows up sometimes in places you don’t expect. In this case, it showed up on my couch.
Which brings me to the follow-up video I recently posted. Because I went back to Gabo and tried something. And that's where things got interesting in a way I wasn't entirely expecting.
Without giving too much away, a simple, carefully worded prompt was enough to shift Gabo’s behavior in a way the toy’s creators almost certainly didn’t intend. What started as a children’s storytelling companion became something else entirely. The result was harmless and honestly a little funny, but the implication for anyone building AI systems is anything but.
Here’s the broader point. Most people’s experience with AI comes through consumer products, the major chat tools that have become household names. What isn’t obvious is how much work those platforms do behind the scenes to shape, monitor, and constrain AI behavior. There are layers of protection most users never see and never need to think about.
When a company builds its own AI solution, those layers aren’t automatically included. The model might be the same, but the managed experience is not. And that gap between what people assume is protected and what actually is protected is where real risk lives. Gabo illustrates this in a way that is surprisingly hard to ignore once you see it.
Many custom AI systems are just as susceptible. They just haven’t been tested yet.
It’s easy to look at a toy and wonder how something like this slipped through. But the more useful question is whether the same thing could happen in your own AI deployment, and whether you’d know it if it did. The attack surface grows every time you allow open-ended user input, file uploads, or flexible system behavior. Most organizations building on AI haven’t tested for this seriously, and that gap tends to surface at the worst possible time.
The question I keep returning to is simple. Have you included specific guardrails in your AI solution, or are you relying on them to be there already?
I walk through the full demonstration and what it means for businesses in my two-part video series. The second video especially is something I’d encourage anyone involved in AI development or deployment to watch before it becomes relevant the hard way.
Both videos are on my LinkedIn. Start with the Gabo introduction if you missed it, then watch the follow-up where things take an unexpected turn and the real lesson lands.
I’d love to hear whether this kind of vulnerability is on your radar and what you’re doing about it. Reach out to me on LinkedIn to share your thoughts.